GitHub makes AI Scan for pull requests generally available
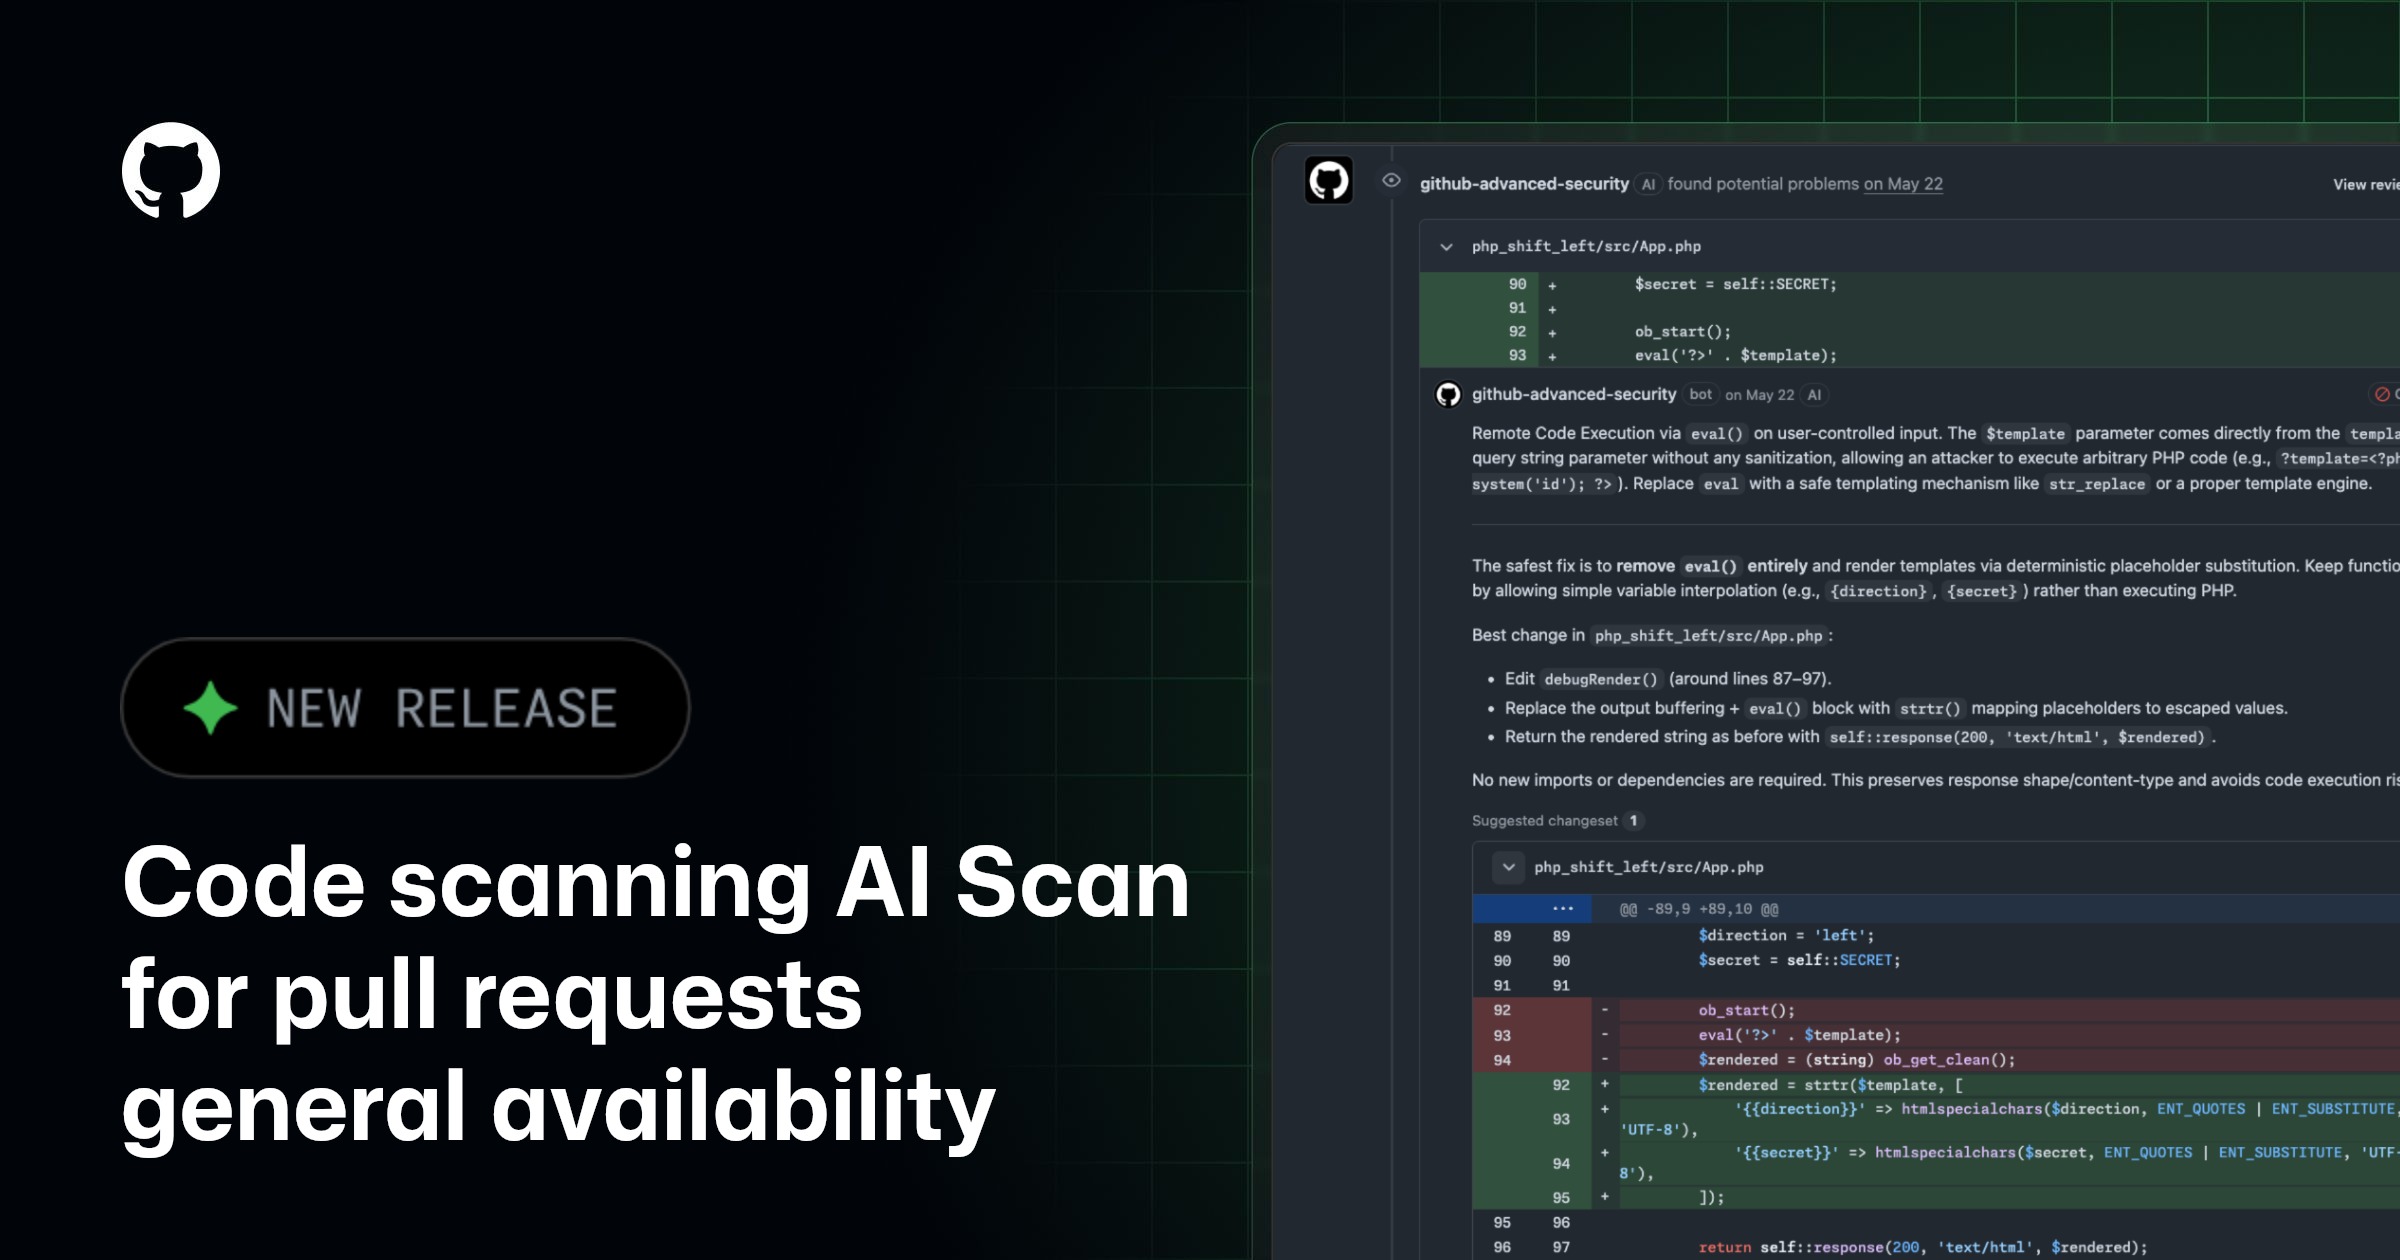
GitHub announced that AI Scan for pull requests in code scanning is now generally available. The feature complements CodeQL by finding vulnerabilities in pull request changes for languages and frameworks that CodeQL does not currently cover.
Why it matters
Teams using languages or frameworks outside CodeQL's coverage can extend pull request security scanning to those codebases without waiting for CodeQL support.
Who should care
Software development teams, security engineers, and maintainers of repositories on GitHub using code scanning.
What you can do
Check whether your repositories use languages or frameworks not covered by CodeQL, and enable AI Scan for pull requests in code scanning settings to review those changes.