Supabase announces per-app MCP servers where tool calls run as the signed-in user
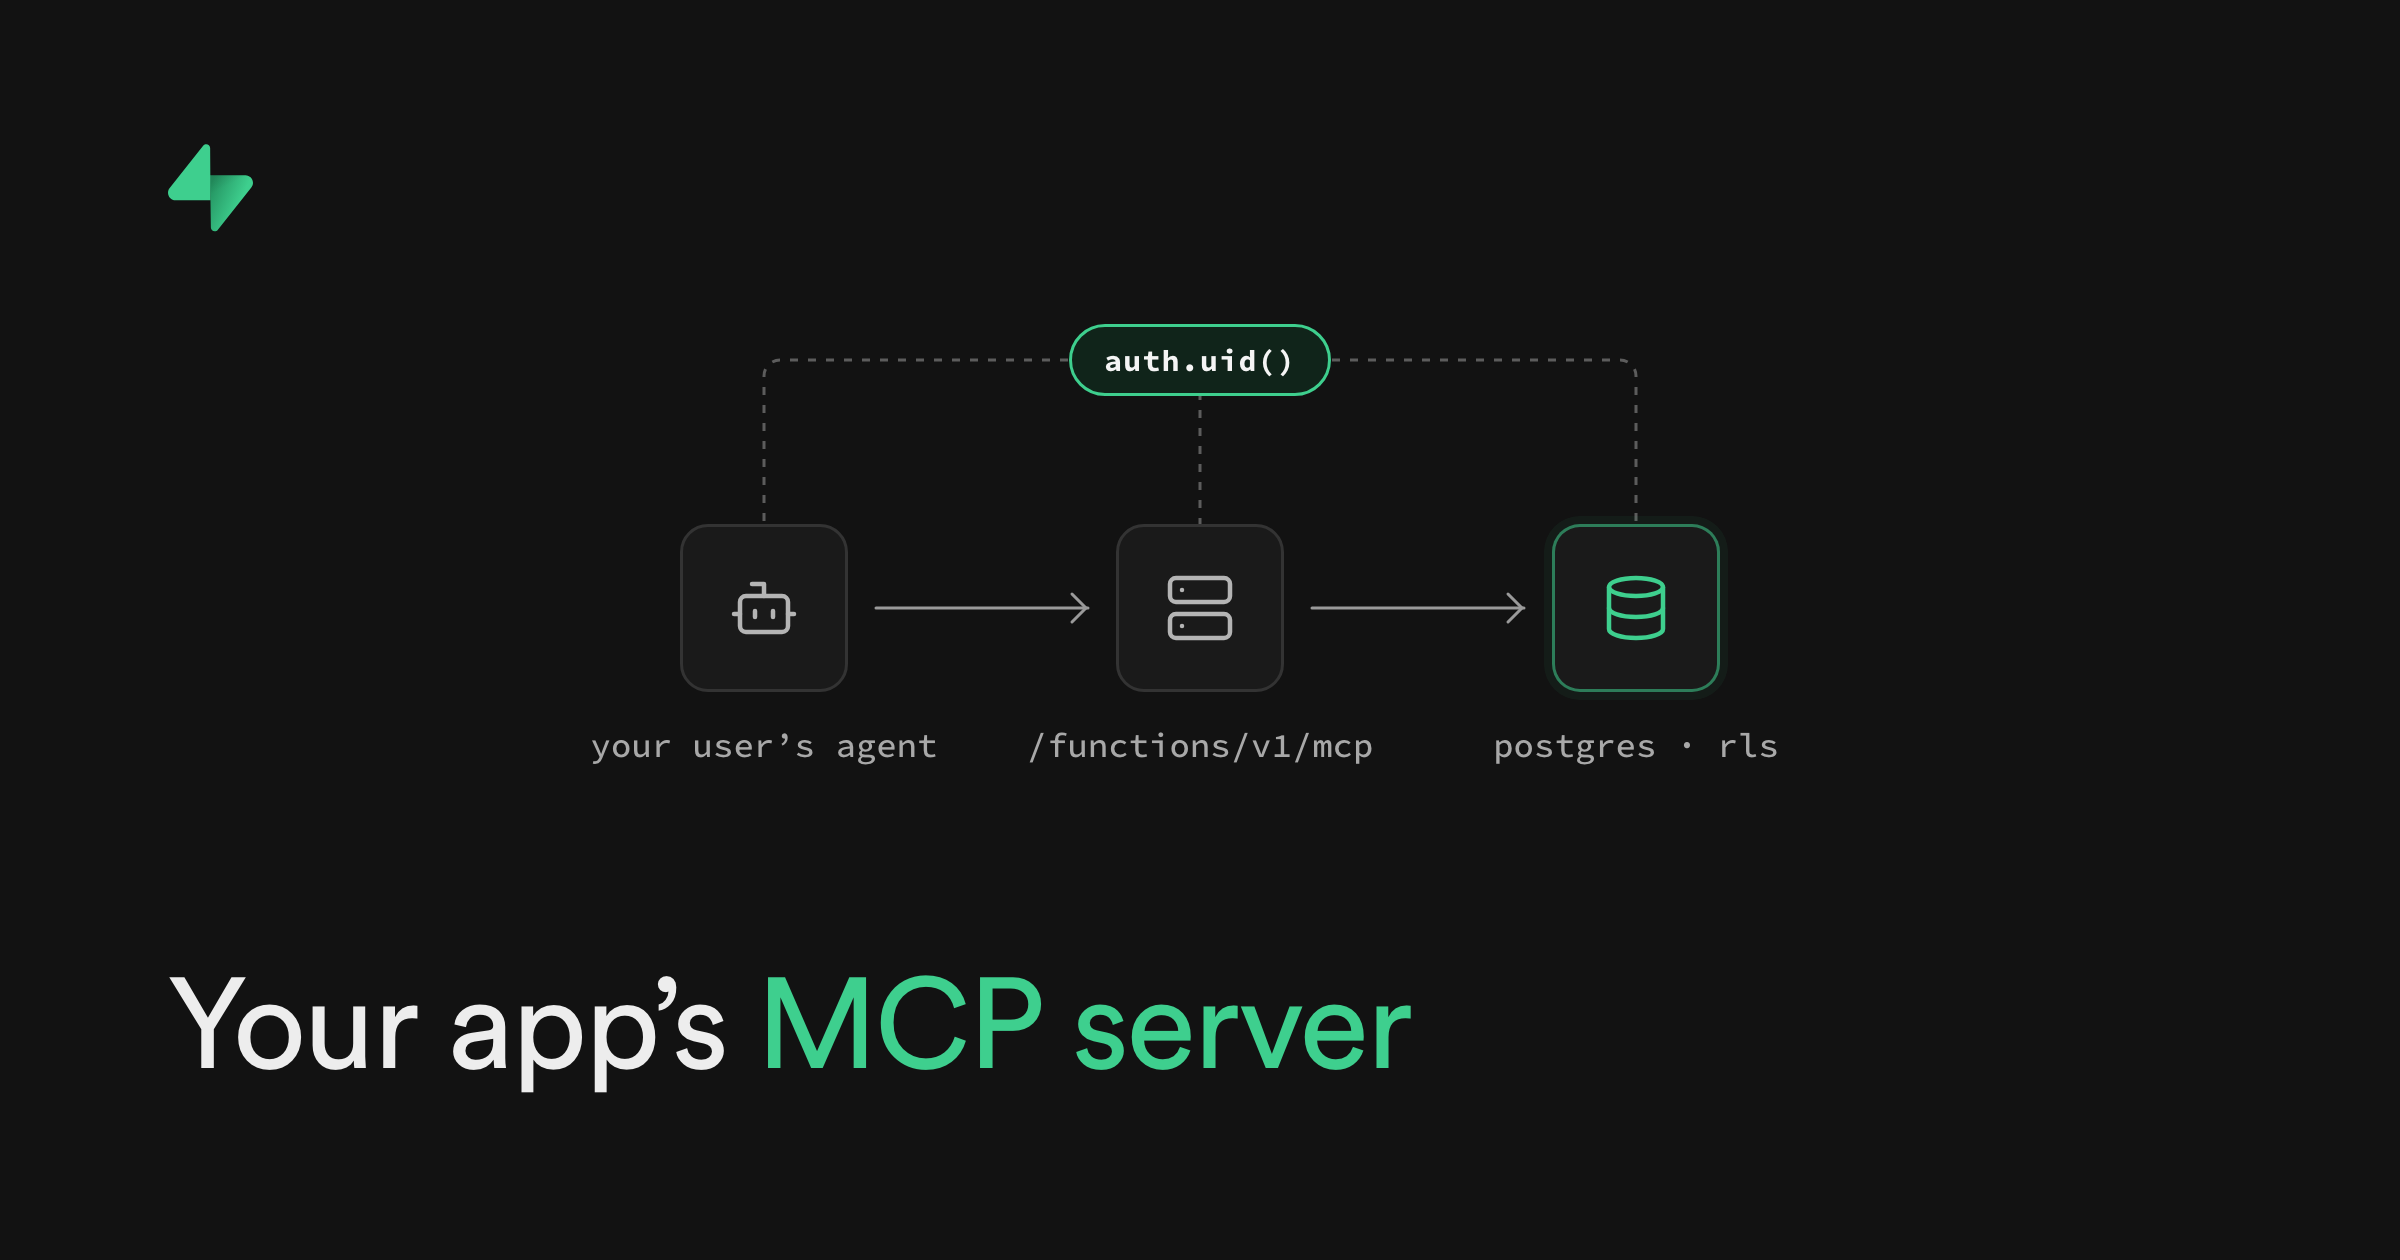
Supabase published a blog post introducing the ability to give a Supabase app its own MCP server. Per the post, every tool call runs as the signed-in user, so existing Row Level Security (RLS) policies determine what each agent can access.
Why it matters
Access control for AI agents connected to a Supabase app is enforced by the RLS policies already written for that app, rather than a separate permission layer. Builders who have already defined RLS policies may not need to write additional agent-specific authorization logic.
Who should care
Developers building apps on Supabase, teams exposing app data or actions to AI agents via MCP, ecommerce and SaaS builders with user-scoped data.
What you can do
Review your RLS policies on tables an agent would access, then test an MCP connection while signed in as a test user to confirm the agent sees only the rows that user is permitted to see.