GitHub makes agentic autofix for code scanning alerts generally available
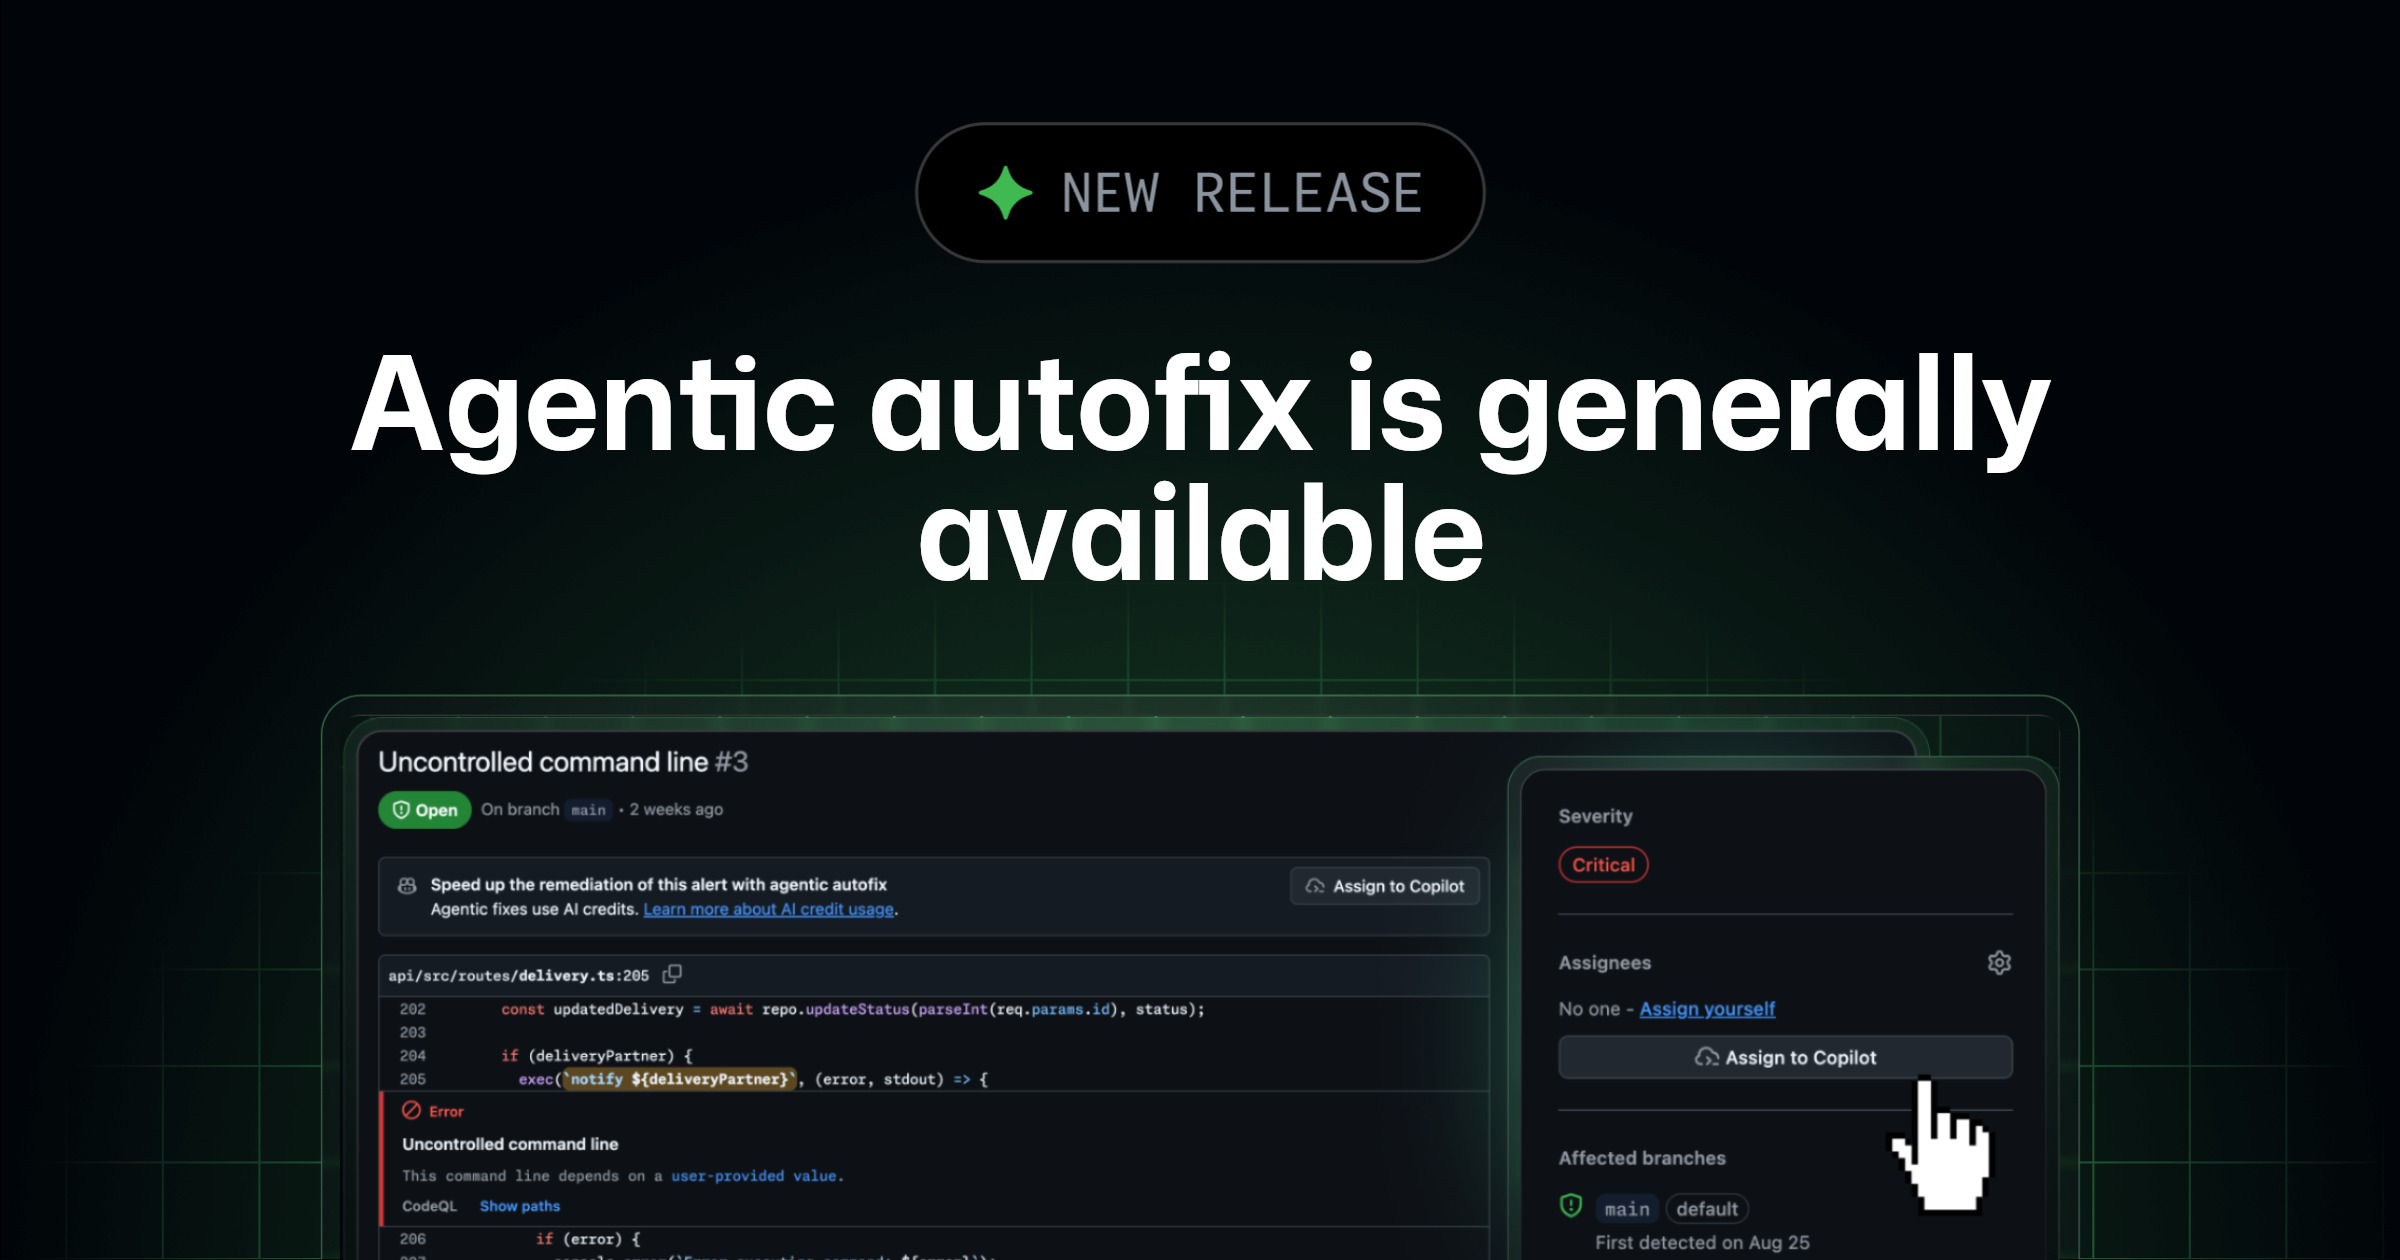
GitHub announced general availability of agentic autofix for code scanning alerts. The feature remediates alerts by exploring relevant files across a codebase, proposing a fix, and working through changes similarly to a developer.
Why it matters
Teams using GitHub code scanning can now use an agent-based autofix workflow on alerts rather than only manual remediation. This may reduce time spent triaging and fixing security findings in repositories that ship customer-facing sites, apps, or integrations.
Who should care
Software developers, security engineers, DevOps teams, and engineering leads at online businesses using GitHub code scanning.
What you can do
Enable code scanning on a key repository, review the autofix proposals on open alerts, and check the generated changes against your test suite before merging.