Vercel Connect adds Secure Compute routing for providers with IP allowlists
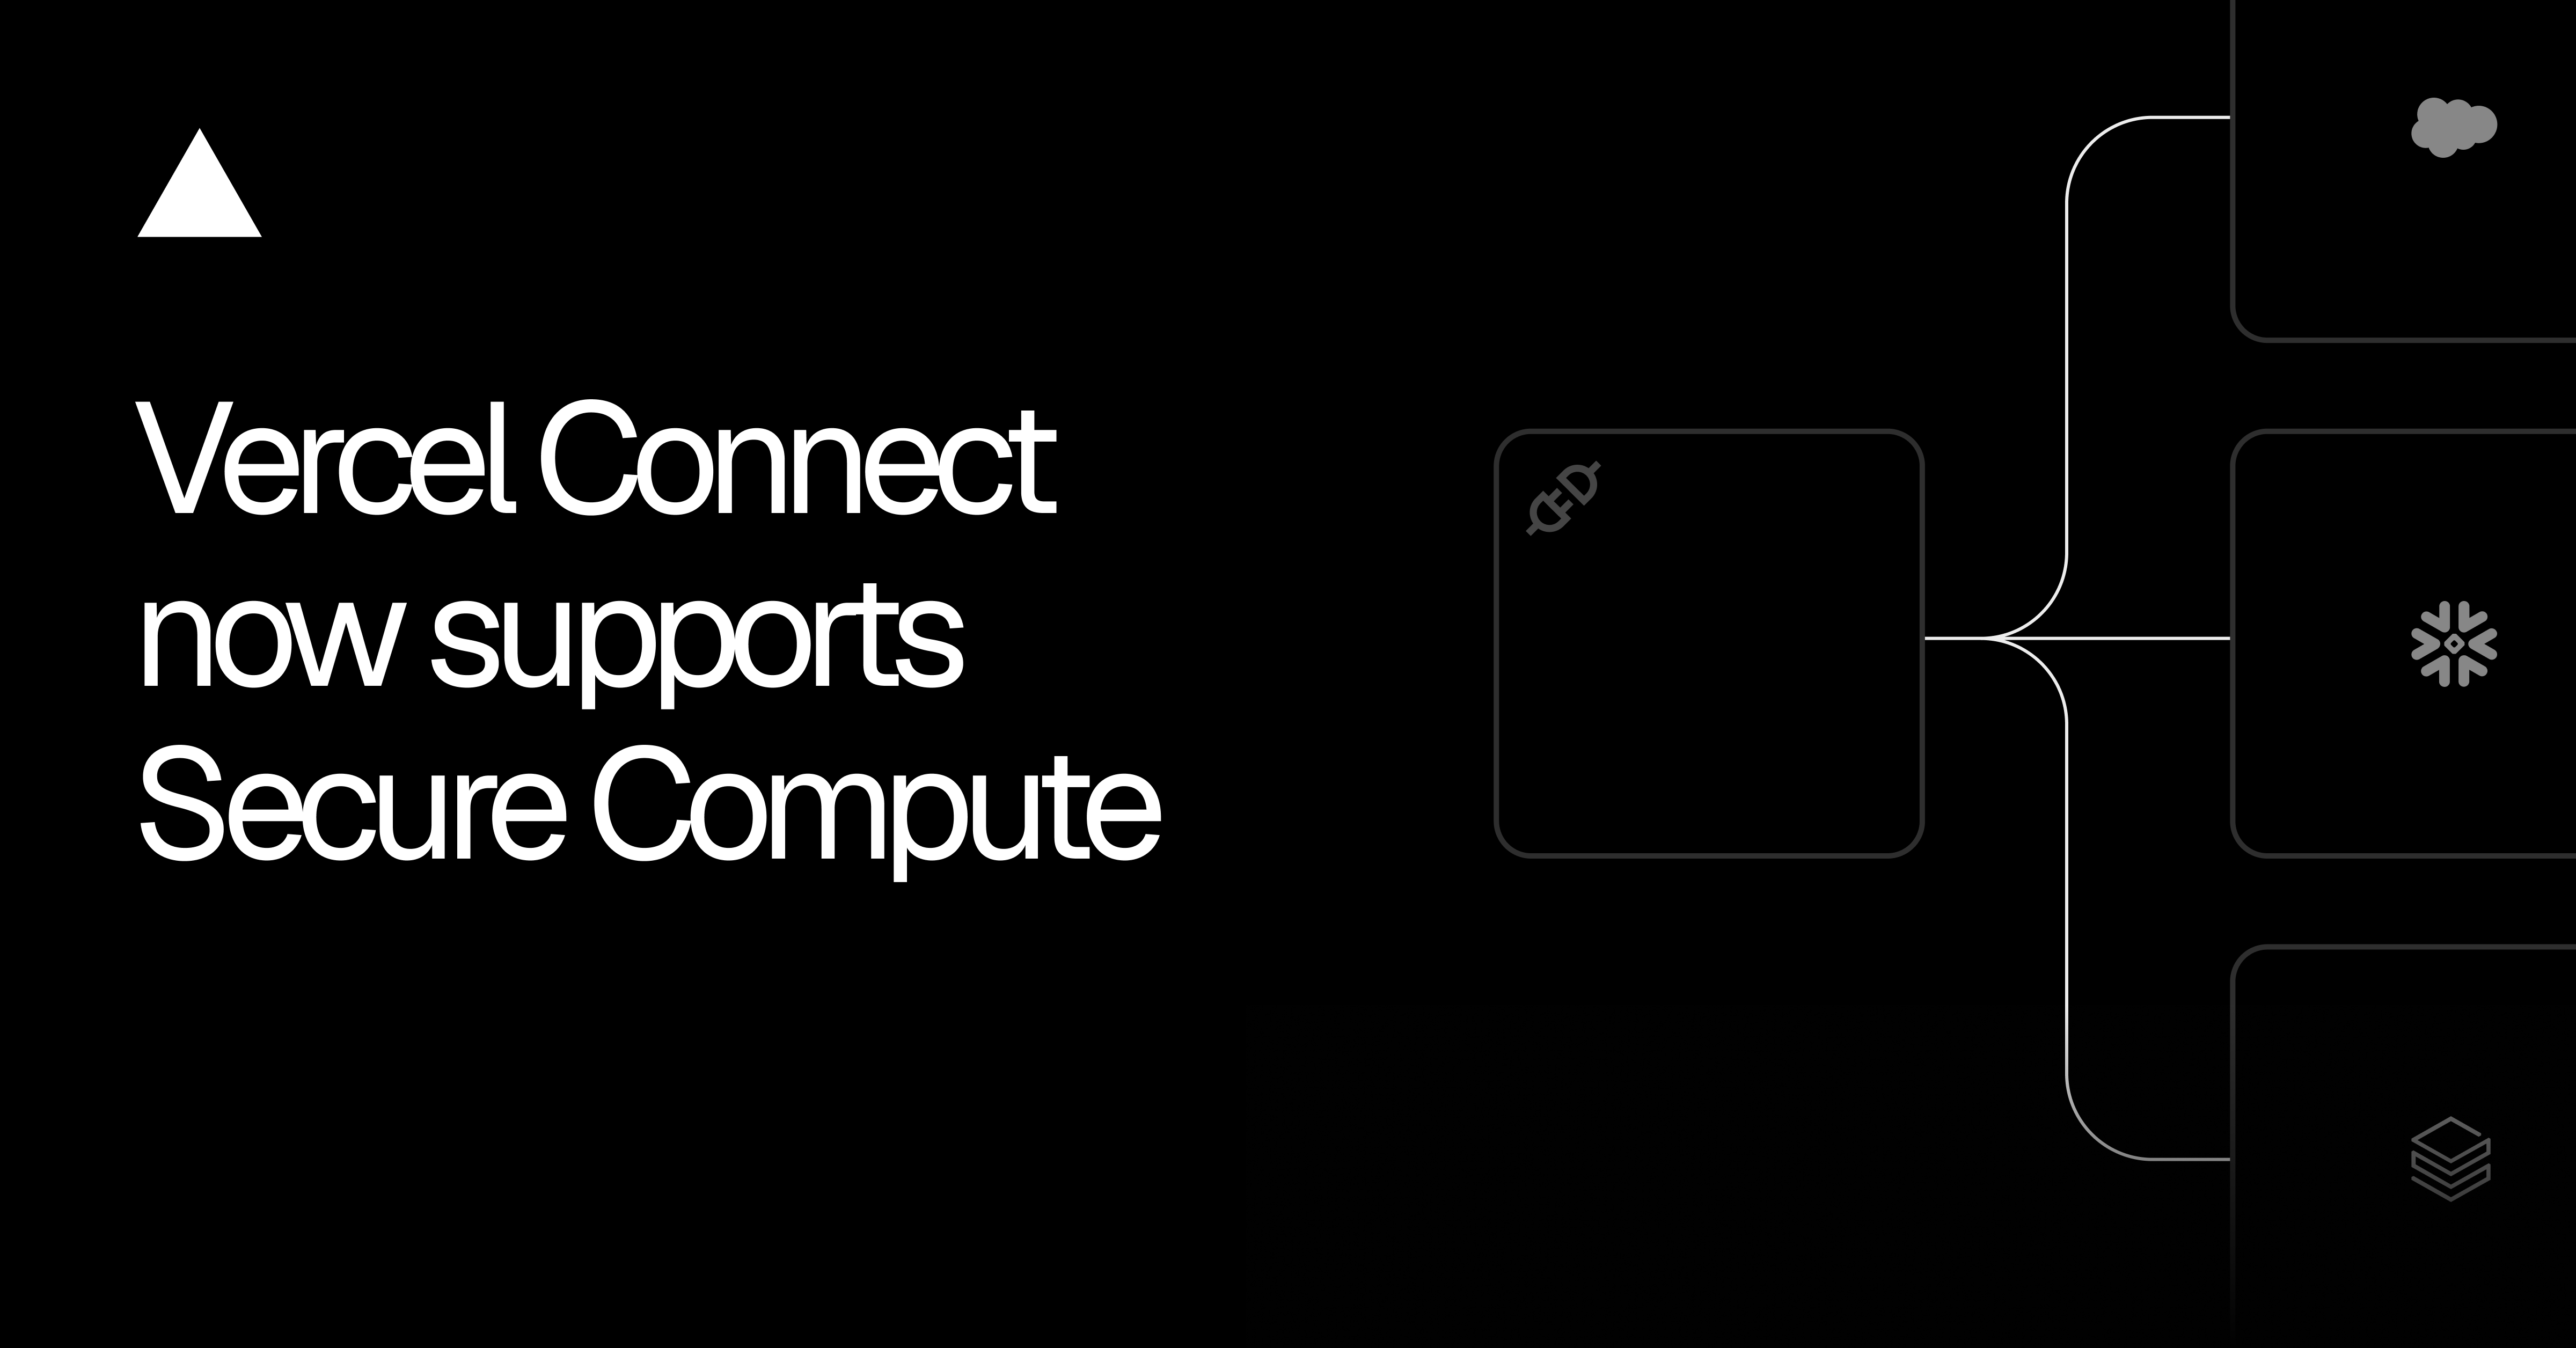
Vercel Connect now supports Secure Compute. With Secure Compute routing enabled on a connector, Connect's provider requests, including token obtain and refresh requests, use the selected network's dedicated static IP addresses instead of Connect's shared IPs. Requests for initial connector creation and provider discovery bypass the selected network, and routed requests fail if the network is unavailable rather than falling back to shared IPs.
Why it matters
Providers that restrict access by IP allowlist, such as Salesforce and Snowflake, can now be connected through Vercel Connect without storing long-lived provider secrets in the app or building custom OAuth flows. Builders need to register the network's static IPs with the provider for routed requests to succeed.
Who should care
Developers and teams building apps on Vercel that integrate with IP-restricted providers such as Salesforce and Snowflake.
What you can do
In the Vercel dashboard, open a connector's Settings, choose an existing Secure Compute network under Secure Compute Routing, add the displayed IP addresses to the provider's IP allowlist, and save the changes in Connect.